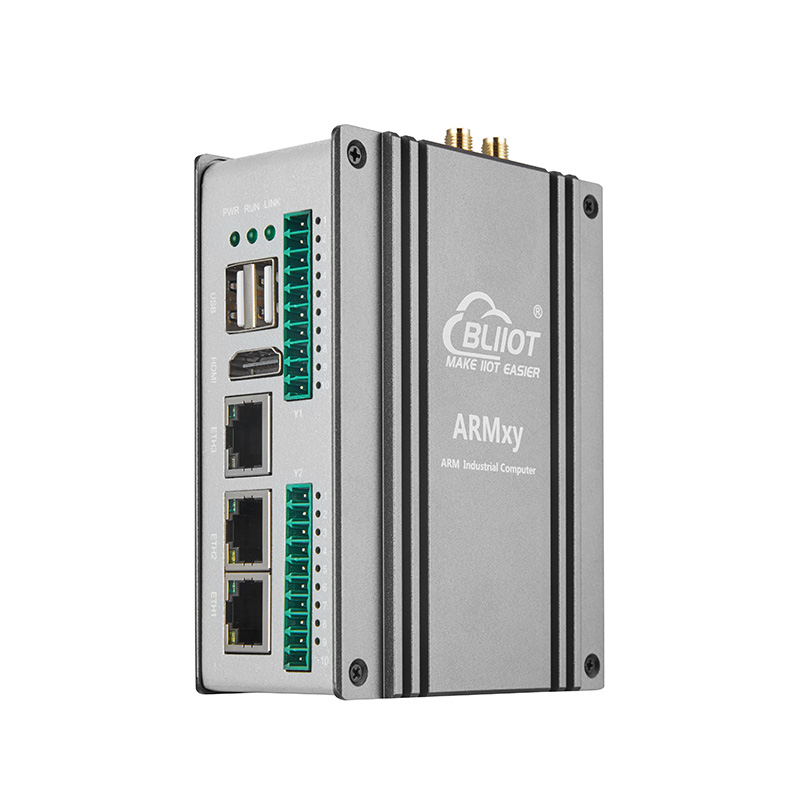
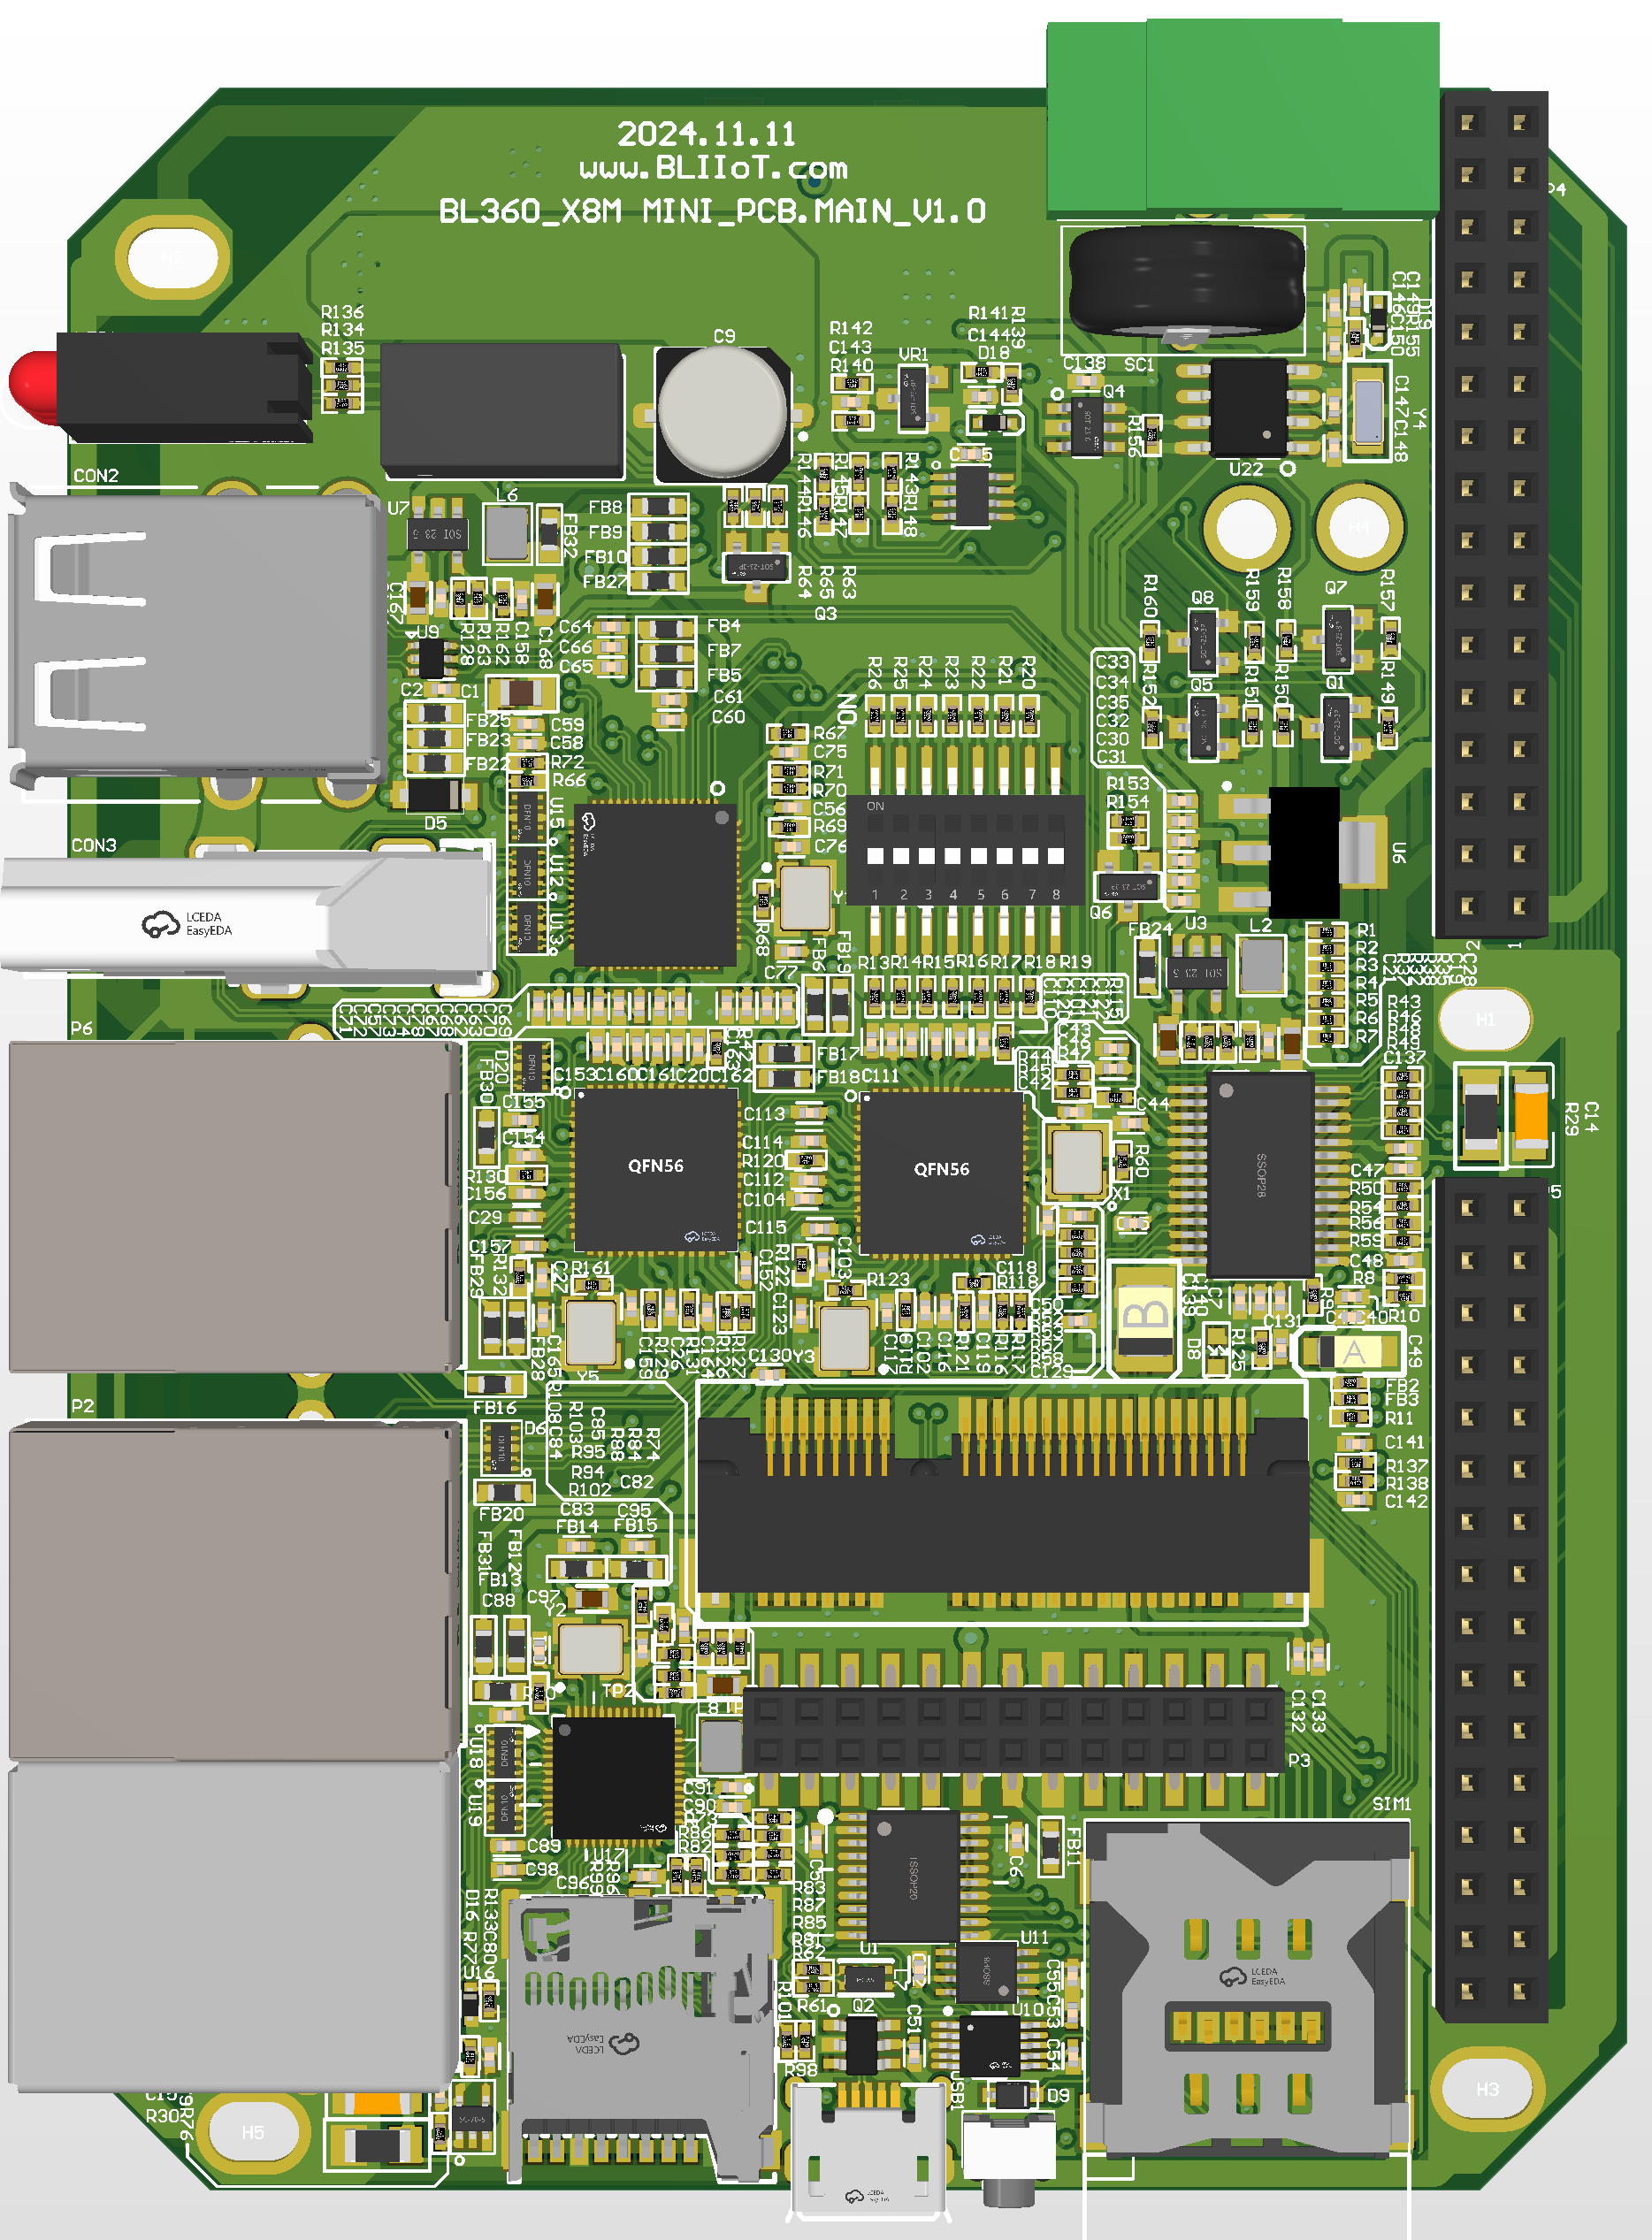
Raspberry Pi CM5-based ARMxy BL460 platform integrates ST33KTPM2X TPM 2.0 for hardware-based key protection, device identity, and platform integrity.
Hardware-backed security for cryptographic key protection, device identity, and platform integrity.
As industrial edge devices connect to enterprise networks, cloud platforms, and remote management systems, protecting device credentials and software integrity becomes increasingly important.
To address these requirements at the hardware level, BEILAI has integrated a TPM 2.0 security chip into its Raspberry Pi CM5-based ARMxy BL460 industrial computer.
This integration provides a dedicated hardware security component that developers can incorporate into their industrial security architecture.
1. Why TPM 2.0 Matters for Industrial Computing
A Trusted Platform Module (TPM) is a dedicated security component designed to support cryptographic operations, protected key management, and platform integrity mechanisms.
Unlike approaches that rely exclusively on software-managed security, TPM 2.0 provides hardware-backed functions that can help reduce exposure of sensitive cryptographic keys and establish a foundation for device authentication and trusted platform verification.
For industrial applications, these capabilities are particularly relevant when devices need to authenticate to remote services, protect credentials, or operate within a managed security environment.
2. Three Key Security Capabilities
The TPM 2.0 chip integrated into the BL460 is the ST33KTPM2X from STMicroelectronics' STSAFE-TPM family. It supports the TPM 2.0 specification and provides dedicated hardware support for multiple cryptographic functions.
Cryptographic Key Protection
Cryptographic keys underpin device authentication, digital signatures, and encrypted communication.
TPM 2.0 supports hardware-backed key generation and management, allowing suitable private keys to remain protected within the TPM environment rather than being exposed as ordinary files in the operating system.
This can support device authentication, certificate-based communication, and TPM-backed encryption architectures. Actual protection depends on key configuration, provisioning, authorization, and application integration.
Platform Integrity
A device's security depends partly on whether its firmware and software start in an expected state.
TPM 2.0 provides Platform Configuration Registers (PCRs) that can record measurements of selected platform components. When combined with an appropriately configured startup process, these measurements can support platform integrity assessment and measured boot.
TPM-based measurements can also contribute to remote attestation and policies that restrict access to sensitive keys.
TPM measurement is not the same as Secure Boot. Secure Boot verifies authorized boot components, while measured boot records measurements for subsequent evaluation. The mechanisms can complement each other, but the required firmware and software configuration must be implemented separately.
Device Identity and Authentication
Industrial devices deployed across multiple sites often need individual identities for enrollment, authentication, and access management.
TPM-backed keys can support device identity and certificate-based authentication when combined with appropriate provisioning and software infrastructure.
For OEM manufacturers and distributed edge deployments, this provides a foundation for managing device credentials and authenticated connections throughout the device lifecycle.
3. Security Features at the Hardware Level
The integrated ST33KTPM2X incorporates security-oriented hardware features designed to strengthen the protection of cryptographic operations.
According to STMicroelectronics' datasheet, these include:
- Active shielding and environmental monitoring to support hardware protection and detection of abnormal operating conditions.
- Countermeasures against fault-injection and side-channel attacks to help protect sensitive security operations.
- Dedicated random-number generation, including true random-number generation and deterministic random-bit generation capabilities.
The chip supports cryptographic algorithms including RSA, elliptic-curve cryptography (ECC), AES, SHA-family hashing, and HMAC.
These features demonstrate an important principle of hardware security: strong cryptographic algorithms need to be complemented by appropriate key protection, implementation safeguards, and system-level controls.
4. Bringing TPM 2.0 to a Raspberry Pi CM5 Industrial Computer
The BLIIOT ARMxy BL460 is an industrial embedded computer based on the Raspberry Pi Compute Module 5 and Broadcom BCM2712 quad-core Cortex-A76 processor.
It combines the Raspberry Pi computing ecosystem with industrial-oriented hardware integration, including Ethernet connectivity, USB 3.0, and configurable X/Y I/O expansion.
With TPM 2.0, the platform offers an additional hardware security option for projects requiring:
- Industrial IoT gateways: Hardware-backed credentials for authenticated communication.
- Edge computing systems: Protection of cryptographic keys used in applications processing sensitive operational data.
- OEM embedded products: A foundation for device identity, secure enrollment, and project-specific security architectures.
- Distributed equipment deployments: Support for individual device authentication and lifecycle management.
The appropriate implementation depends on each project's security requirements, threat model, operating system, and supporting infrastructure.
5. From Hardware Integration to System-Level Security
TPM 2.0 provides important hardware security capabilities, but integrating the chip alone does not automatically enable every security function.
A complete implementation may require:
- TPM initialization, provisioning, and key lifecycle management
- Firmware and bootloader configuration, including Secure Boot where supported
- Linux TPM drivers and the required software stack
- Storage encryption and TPM-backed key-release policies, where required
- Application-level authentication, secure updates, and ongoing security maintenance
These elements must be designed and validated as part of the complete system. For example, full-disk encryption and remote attestation require additional software and infrastructure; they are not automatically enabled by the presence of a TPM.
For OEM projects, defining these requirements early helps establish the appropriate division of responsibilities between hardware, firmware, operating systems, applications, and management platforms.
A Hardware Security Foundation for Industrial Edge Devices
By integrating the ST33KTPM2X TPM 2.0 security component into its Raspberry Pi CM5-based ARMxy BL460 platform, BEILAI provides an additional hardware foundation for developers building industrial systems that require cryptographic key protection, device identity, and platform integrity capabilities.
BLIIOT Raspberry Pi Industrial Computer with TPM 2.0: Hardware-backed security for industrial edge computing.
Contact BEILAI to discuss hardware configurations and software integration requirements for your industrial security project.